Recent posts

The dangerous time to discover a role problem is after go-live
A role change can look harmless. A new transaction.A new authorization object.A new assignment.A small adjustment to support a project. Then it goes...
Nov 06, 2026
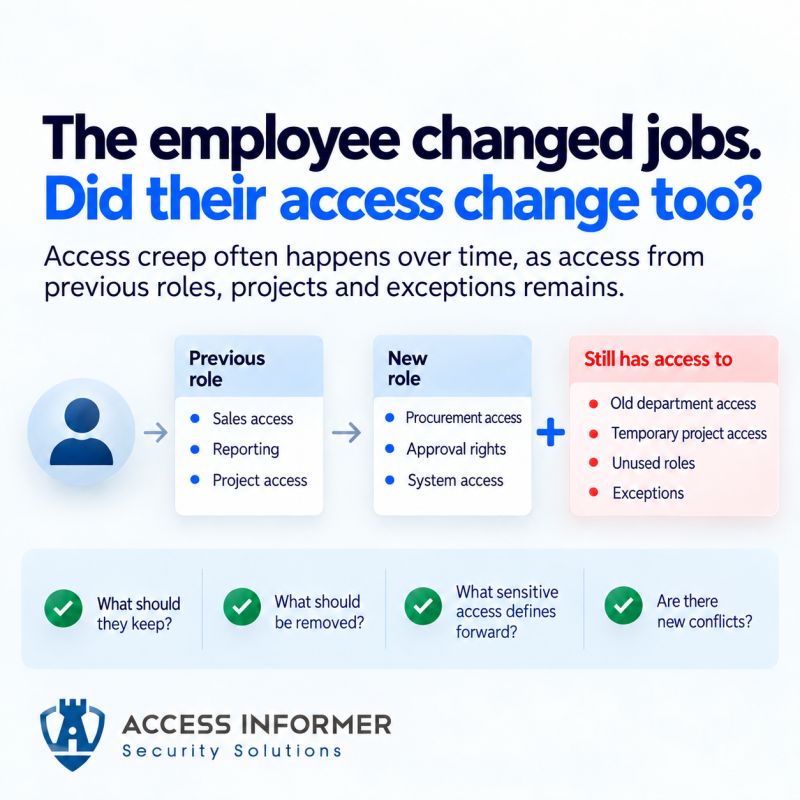
The employee change jobs. Did their access change too?
This is one of the simplest ways access creep happens. Someone moves from one department to another. They receive the access required for the new...
Nov 02, 2026
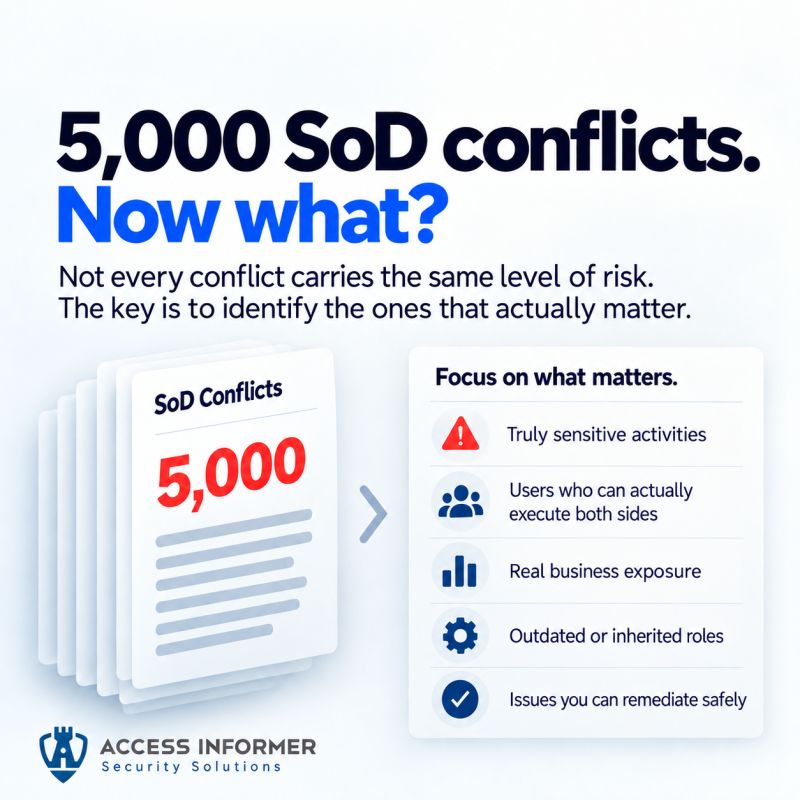
5 000 SOD conflicts. Now what?
I've seen SoD exercises generate enormous numbers of findings. Hundreds. Thousands. Sometimes far more. And technically, the report may be correct....
Oct 30, 2026
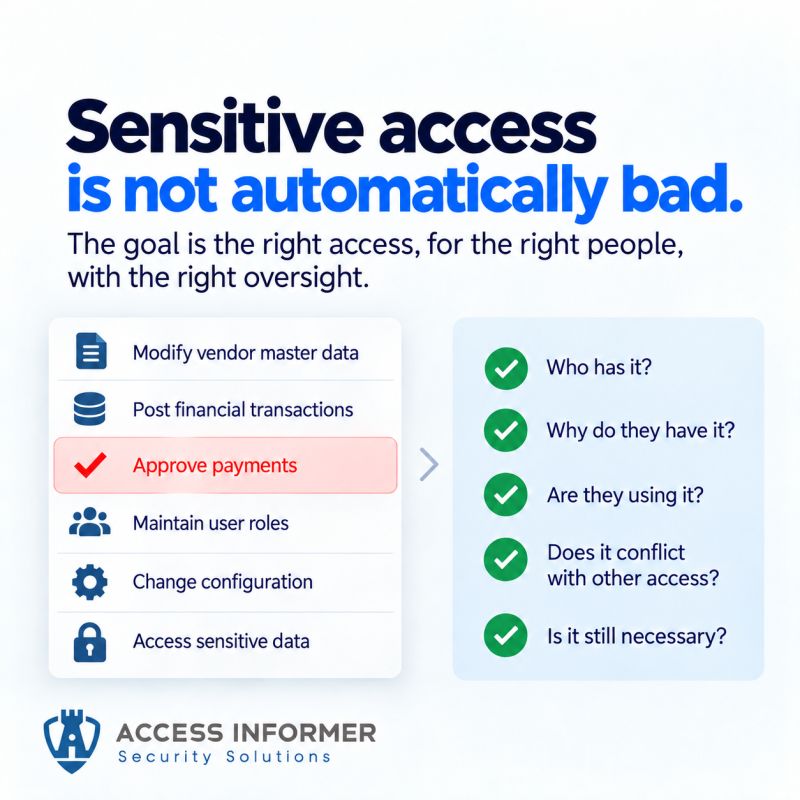
Sensitive access is not automatically bad
I don't believe the goal of SAP security should be to eliminate sensitive access. That wouldn't be realistic. People need to perform critical...
Oct 28, 2026
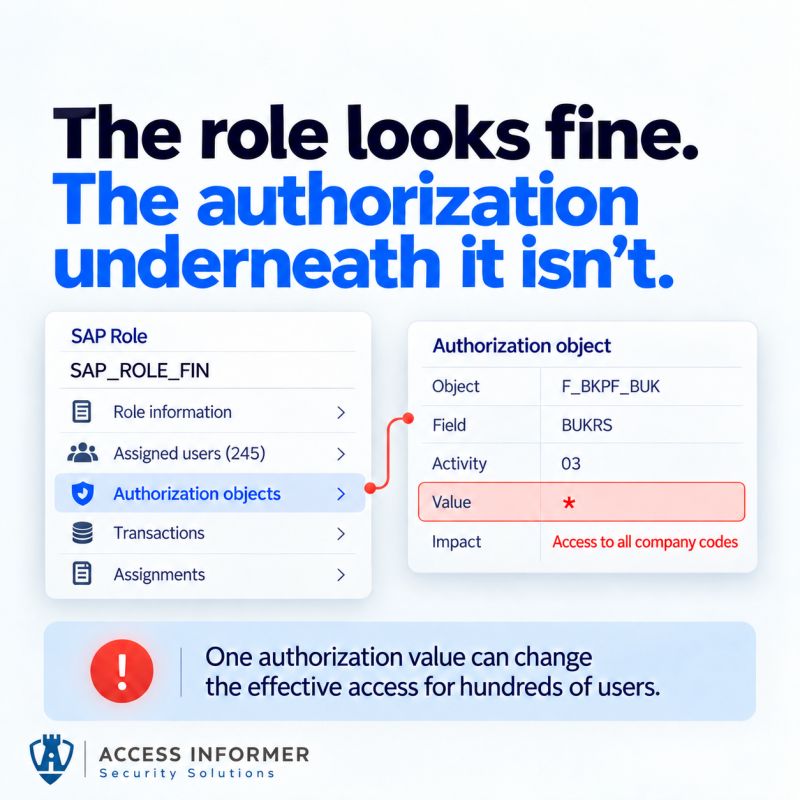
The role looks fine
A role can look perfectly reasonable on paper. The name makes sense.The assignment was approved.The user clearly needs it. And yet the real issue...
Oct 23, 2026
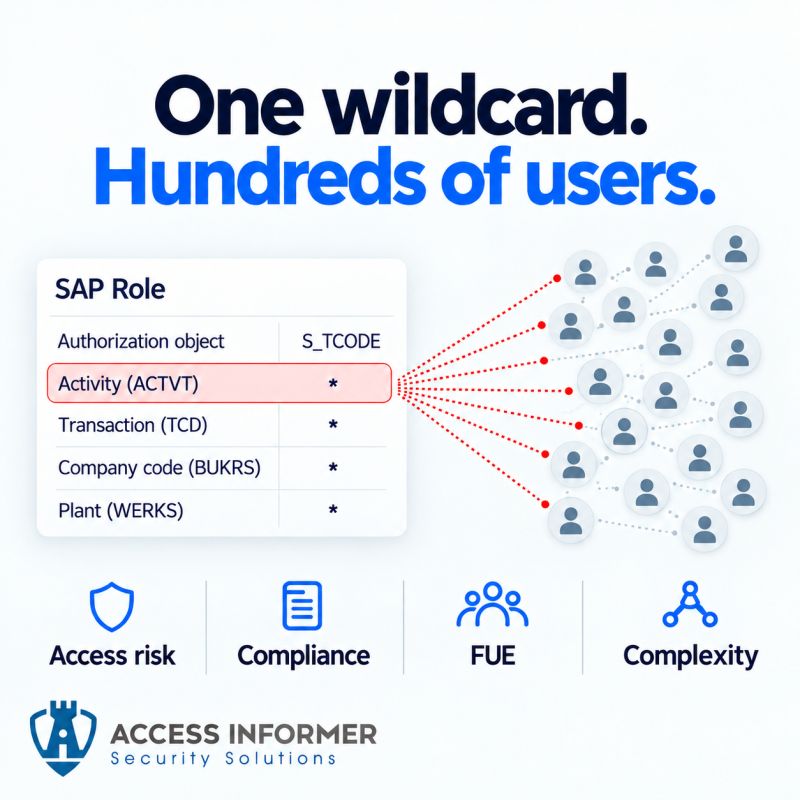
One Wildcard. Hundreds of users
When reviewing SAP access, people naturally look at roles. Which roles does the user have? Are the roles approved? Does the role name make sense?...
Oct 21, 2026