When reviewing SAP access, people naturally look at roles.
Which roles does the user have?
Are the roles approved?
Does the role name make sense?
All useful questions.
But sometimes the interesting part isn’t the role.
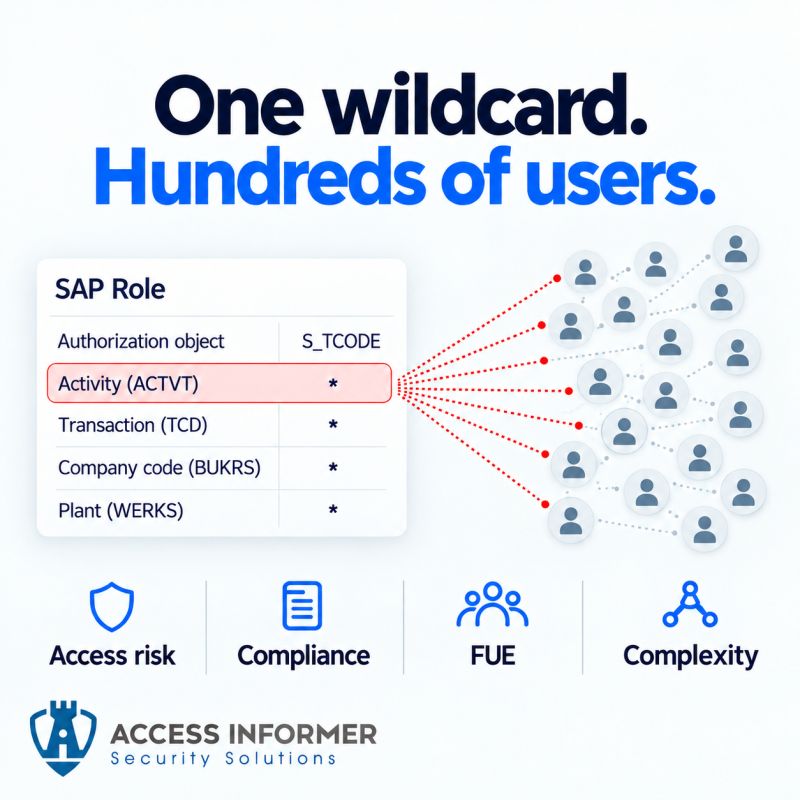
It’s what is sitting 𝗶𝗻𝘀𝗶𝗱𝗲 it.
• A wildcard
• A broad range
• An authorization value that is much wider than the business requirement
And suddenly an otherwise ordinary role gives someone access well beyond what everyone assumes they have.
This is why high-level role reviews can create a false sense of comfort.
The role might be completely legitimate.
The user might genuinely need the role.
The problem can be one small piece of authorization content underneath it.
And that small detail can affect hundreds of users if the role is widely assigned.
The same issue can also have consequences beyond security.
We see situations where specific authorization objects or values contribute to a user’s FUE classification.
So one configuration decision can potentially affect:
• Access risk
• Compliance
• Role complexity
• Licensing cost
All from the same underlying authorization.
This is the level of detail I think SAP security teams need to be able to see quickly.
Not simply:
❌ “𝗪𝗵𝗶𝗰𝗵 𝗿𝗼𝗹𝗲 𝗶𝘀 𝘄𝗿𝗼𝗻𝗴?”
But:
✅ “𝗪𝗵𝗮𝘁 𝗲𝘅𝗮𝗰𝘁𝗹𝘆 𝗶𝗻𝘀𝗶𝗱𝗲 𝘁𝗵𝗲 𝗿𝗼𝗹𝗲 𝗶𝘀 𝗰𝗿𝗲𝗮𝘁𝗶𝗻𝗴 𝘁𝗵𝗲 𝗽𝗿𝗼𝗯𝗹𝗲𝗺?”
That’s where the useful conversation starts.