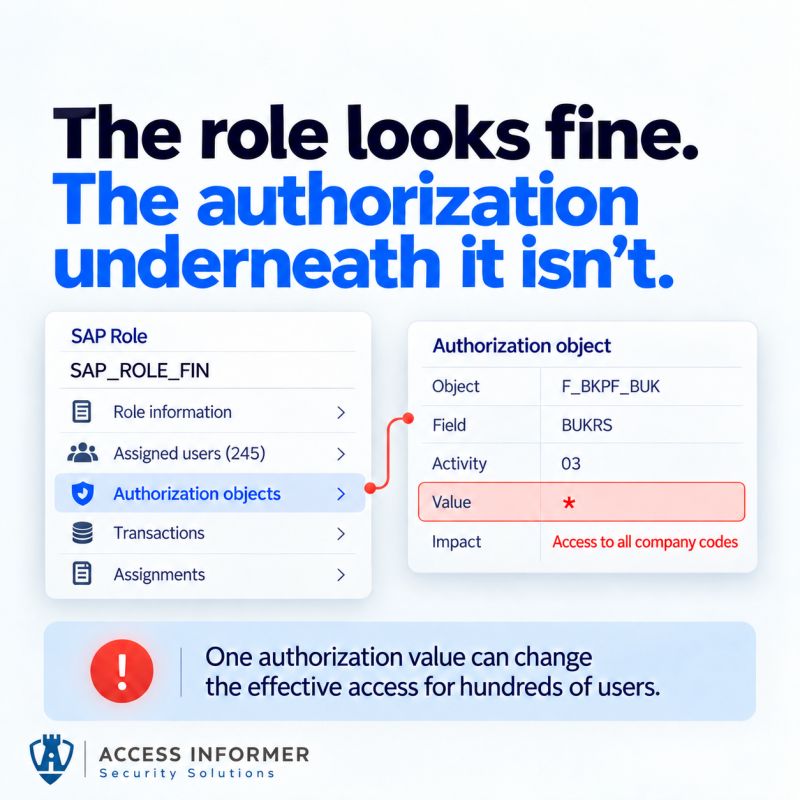
A role can look perfectly reasonable on paper.
The name makes sense.
The assignment was approved.
The user clearly needs it.
And yet the real issue may be sitting much deeper inside the role.
One authorization object.
One activity value.
One unrestricted field.
One range that is broader than anyone intended.
That can change the effective access completely.
This is why role-level reviews only tell part of the story.
You also need to understand:
✅ Which authorization objects are creating the access
✅ Which values make that access sensitive
✅ Whether the user actually needs that level of access
✅ Whether the same issue affects many other users
✅ What changes would fix it without breaking the business
In SAP security, the difference between 𝗶𝗻𝘁𝗲𝗻𝗱𝗲𝗱 𝗮𝗰𝗰𝗲𝘀𝘀 and 𝗲𝗳𝗳𝗲𝗰𝘁𝗶𝘃𝗲 𝗮𝗰𝗰𝗲𝘀𝘀 can be very small technically.
But very significant operationally.
Sometimes the most important finding isn’t:
❌ “This role is wrong.”
It’s:
✅ “This one value inside the role is creating the problem.”
And that level of detail is what makes remediation practical.