
by Cyril Hauppert | Oct 30, 2026 | Blog
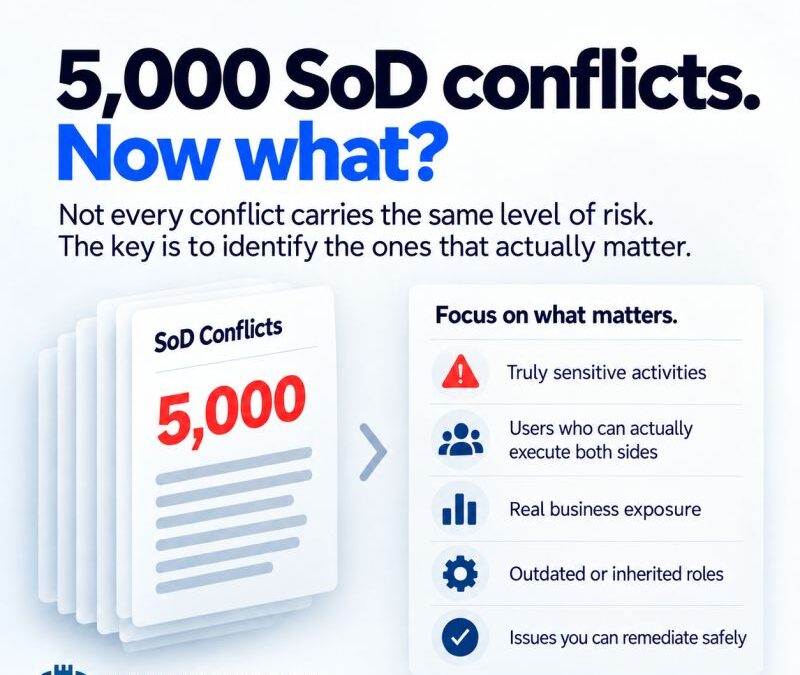
I’ve seen SoD exercises generate enormous numbers of findings. Hundreds. Thousands. Sometimes far more. And technically, the report may be correct. But it leaves the security team with another problem: 𝗪𝗵𝗲𝗿𝗲 𝗱𝗼 𝘆𝗼𝘂 𝘀𝘁𝗮𝗿𝘁? Not every conflict carries the same...
by Cyril Hauppert | Oct 28, 2026 | Blog
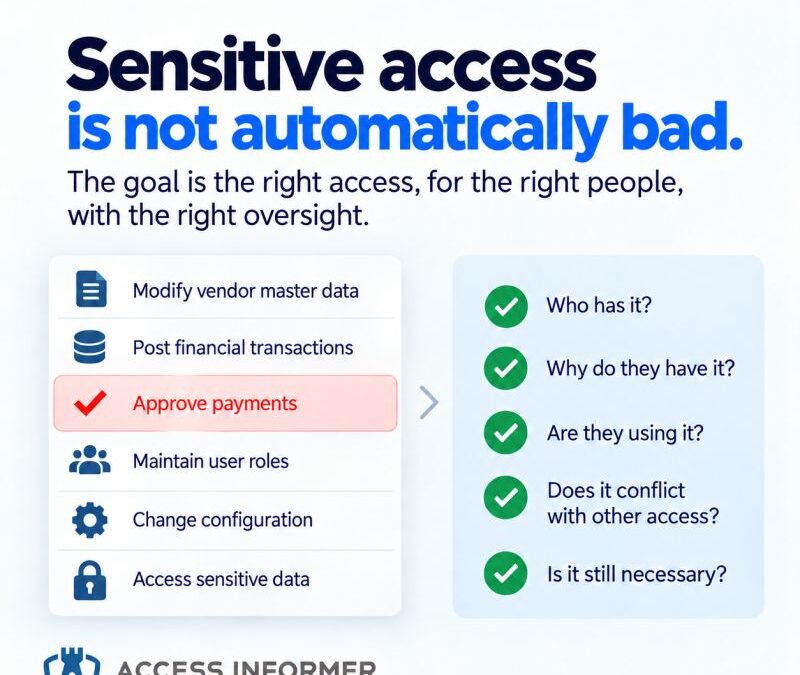
I don’t believe the goal of SAP security should be to eliminate sensitive access. That wouldn’t be realistic. People need to perform critical activities. Someone has to: • Create or change master data• Approve transactions• Administer roles• Maintain...
by Cyril Hauppert | Oct 23, 2026 | Blog
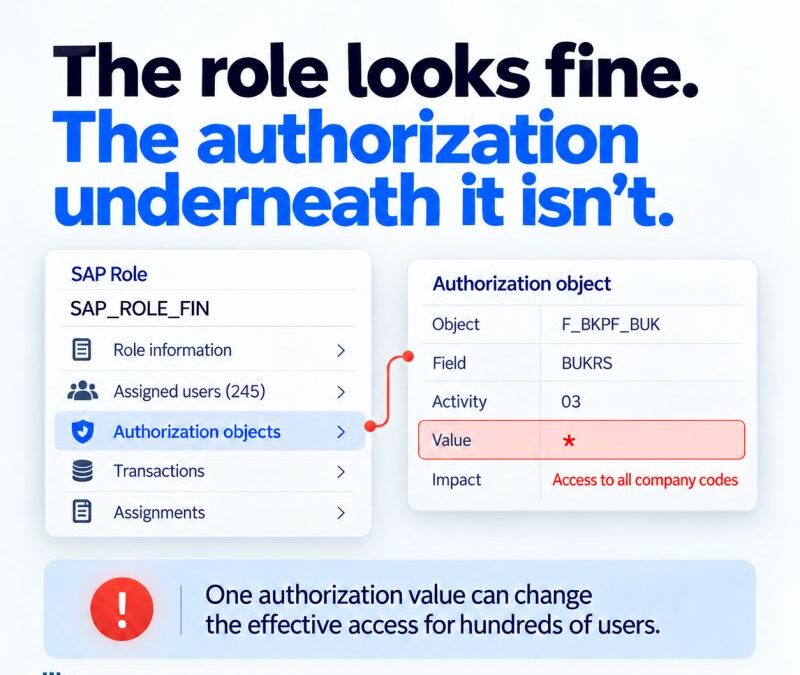
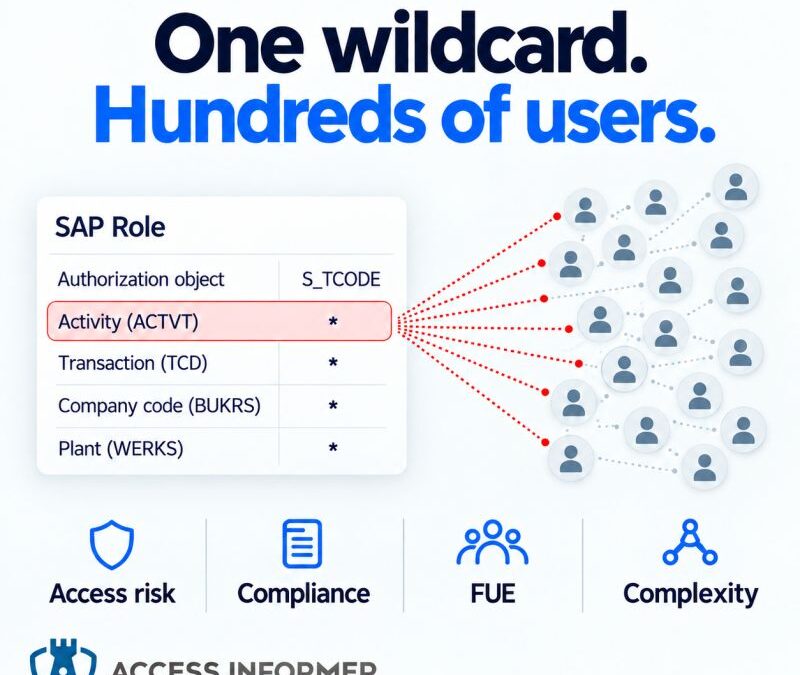
A role can look perfectly reasonable on paper. The name makes sense.The assignment was approved.The user clearly needs it. And yet the real issue may be sitting much deeper inside the role. One authorization object.One activity value.One unrestricted field.One range...
by Cyril Hauppert | Oct 21, 2026 | Blog
When reviewing SAP access, people naturally look at roles. Which roles does the user have? Are the roles approved? Does the role name make sense? All useful questions. But sometimes the interesting part isn’t the role. It’s what is sitting 𝗶𝗻𝘀𝗶𝗱𝗲 it. • A...
by Cyril Hauppert | Oct 19, 2026 | Blog
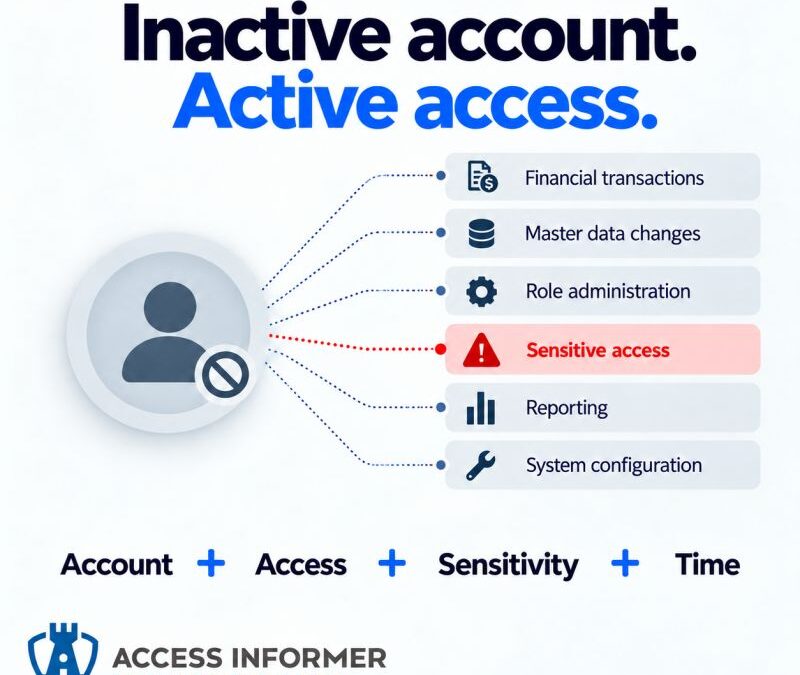
Dormant accounts are easy to categorize as a cleanup problem. An account hasn’t been used. Someone should probably remove it. Put it on the backlog. Move on. But I think that misses the bigger question: 𝗪𝗵𝗮𝘁 𝗮𝗰𝗰𝗲𝘀𝘀 𝗱𝗼𝗲𝘀 𝘁𝗵𝗲 𝗮𝗰𝗰𝗼𝘂𝗻𝘁 𝘀𝘁𝗶𝗹𝗹 𝗵𝗮𝘃𝗲? An unused account...
Recent Comments