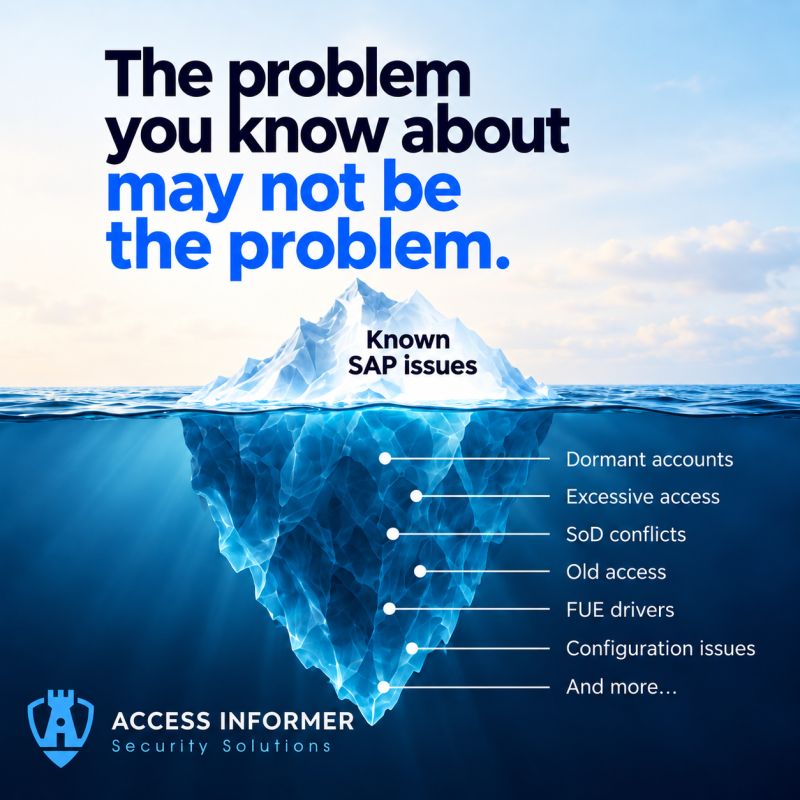
An SAP security issue that has already been discovered is usually not the one that concerns me most.
Once you know it exists, you can investigate it.
You can assign someone to it.
You can remediate it.
You can monitor it.
The more interesting question is:
𝗪𝗵𝗮𝘁 𝗵𝗮𝘃𝗲𝗻’𝘁 𝘆𝗼𝘂 𝗳𝗼𝘂𝗻𝗱 𝘆𝗲𝘁?
Maybe it’s:
• An old account that still has access
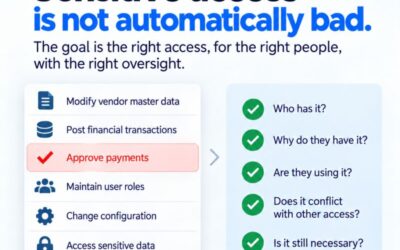
• One authorization value buried inside a role that gives users far more access than expected
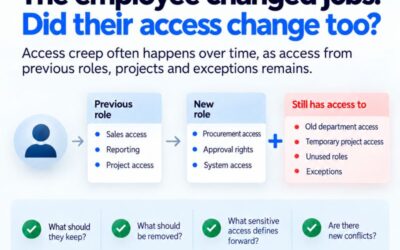
• Someone who moved departments two years ago but still has access from their previous position
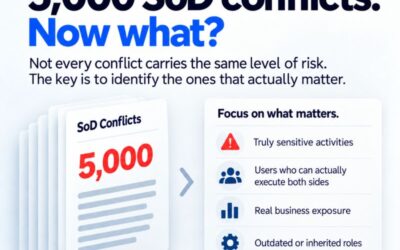
• An apparently harmless role combination that creates a sensitive SoD conflict
• A role that has existed for years and is now driving an unnecessary FUE classification
None of these necessarily causes an obvious operational problem.
That’s exactly why they can remain unnoticed.
SAP environments don’t usually announce:
❌ “𝗬𝗼𝘂 𝗵𝗮𝘃𝗲 𝗮 𝘀𝗲𝗰𝘂𝗿𝗶𝘁𝘆 𝗽𝗿𝗼𝗯𝗹𝗲𝗺.”
Everything keeps running.
Users keep working.
The business continues.
Until someone starts asking deeper questions.
That’s one reason I’m becoming increasingly convinced that SAP security teams need periodic 𝗰𝗿𝗶𝘁𝗶𝗰𝗮𝗹 𝗮𝘀𝘀𝗲𝘀𝘀𝗺𝗲𝗻𝘁𝘀, not simply another large compliance report.
The objective shouldn’t be to generate thousands of findings.
It should be to uncover the handful of things that genuinely deserve attention.