I hear this quite often when talking with SAP security teams:
“𝗪𝗲 𝗵𝗮𝘃𝗲 𝗶𝘁 𝘂𝗻𝗱𝗲𝗿 𝗰𝗼𝗻𝘁𝗿𝗼𝗹.”
And most of the time, I believe them.
The question is what 𝘶𝘯𝘥𝘦𝘳 𝘤𝘰𝘯𝘵𝘳𝘰𝘭 actually means.
Can you see, right now:
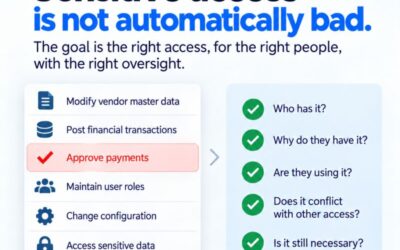
✅ Who has access to sensitive activities?
✅ Which users have access they no longer need?
✅ Where wildcards or broad authorization ranges are creating excessive access?
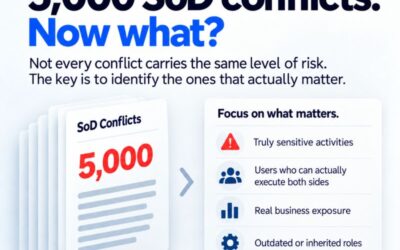
✅ Which SoD conflicts actually represent meaningful risk?
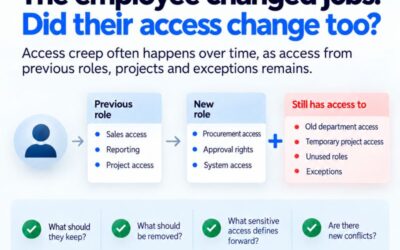
✅ Whether access has been properly removed after employees change positions or leave?
✅ What would happen to your risk profile if you changed a role tomorrow?
The issue isn’t that security teams aren’t doing their jobs.
SAP environments are complex. They have accumulated roles, users, exceptions, organizational changes, and years of decisions.
So a company can have strong processes and still have things hiding underneath the surface.
That’s why one of the first things I like to ask isn’t:
❌ “𝗗𝗼 𝘆𝗼𝘂 𝗵𝗮𝘃𝗲 𝗮𝗻 𝗦𝗔𝗣 𝘀𝗲𝗰𝘂𝗿𝗶𝘁𝘆 𝗽𝗿𝗼𝗯𝗹𝗲𝗺?”
It’s:
✅ “𝗛𝗼𝘄 𝗲𝗮𝘀𝗶𝗹𝘆 𝗰𝗼𝘂𝗹𝗱 𝘆𝗼𝘂 𝗽𝗿𝗼𝘃𝗲 𝘁𝗵𝗮𝘁 𝘆𝗼𝘂 𝗱𝗼𝗻’𝘁?”
Those are two very different questions.
And sometimes the answers are surprising.