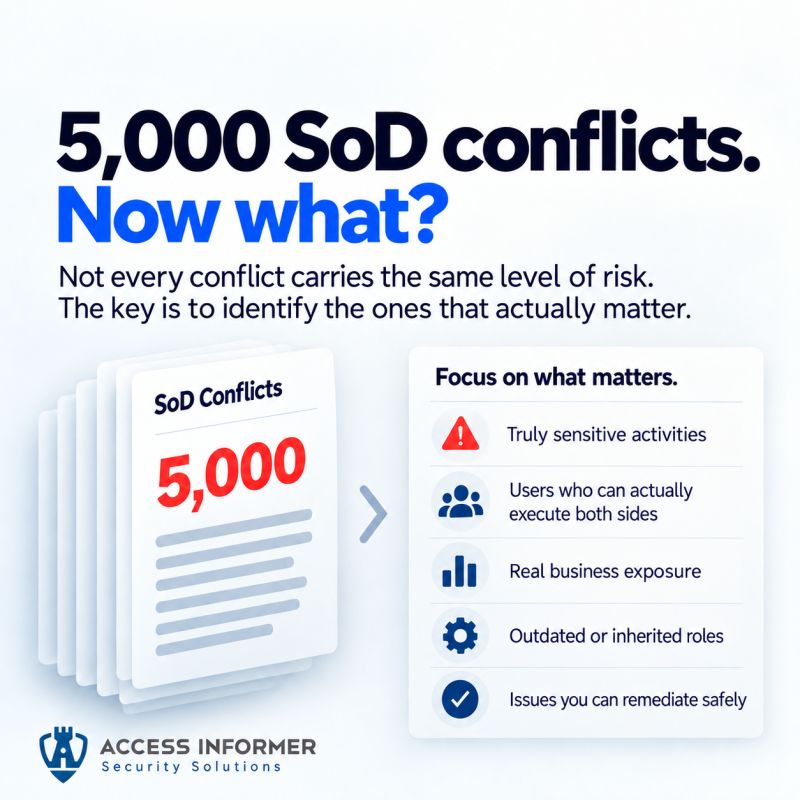
I’ve seen SoD exercises generate enormous numbers of findings.
Hundreds.
Thousands.
Sometimes far more.
And technically, the report may be correct.
But it leaves the security team with another problem:
𝗪𝗵𝗲𝗿𝗲 𝗱𝗼 𝘆𝗼𝘂 𝘀𝘁𝗮𝗿𝘁?
Not every conflict carries the same level of risk.
Not every combination is actually being used.
Not every issue deserves the same urgency.
That means the useful questions become:
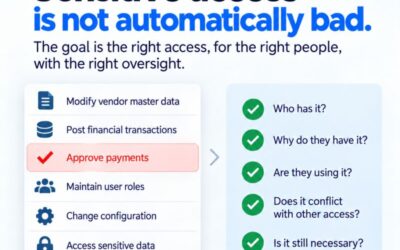
→ Which conflicts involve truly sensitive activities?
→ Which users can actually execute both sides of the conflict?
→ Which combinations represent meaningful business exposure?
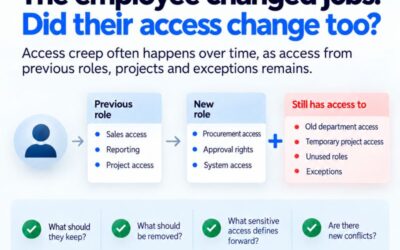
→ Which issues are inherited from old roles or outdated assignments?
→ Which conflicts can be remediated safely without disrupting operations?
This is where I think many compliance exercises lose value.
They focus heavily on 𝗳𝗶𝗻𝗱𝗶𝗻𝗴 𝗲𝘃𝗲𝗿𝘆𝘁𝗵𝗶𝗻𝗴.
But very little on 𝗱𝗲𝗰𝗶𝗱𝗶𝗻𝗴 𝘄𝗵𝗮𝘁 𝗺𝗮𝘁𝘁𝗲𝗿𝘀 𝗺𝗼𝘀𝘁.
For a CISO or SAP security lead, 5,000 findings are not necessarily better than 50.
And 50 may not be better than 5.
If the 5 are the ones that actually matter.
𝗔 𝘂𝘀𝗲𝗳𝘂𝗹 𝗮𝘀𝘀𝗲𝘀𝘀𝗺𝗲𝗻𝘁 𝘀𝗵𝗼𝘂𝗹𝗱 𝗵𝗲𝗹𝗽 𝗽𝗿𝗶𝗼𝗿𝗶𝘁𝗶𝘇𝗲 𝗿𝗶𝘀𝗸, 𝗻𝗼𝘁 𝗷𝘂𝘀𝘁 𝗰𝗼𝘂𝗻𝘁 𝗶𝘁.