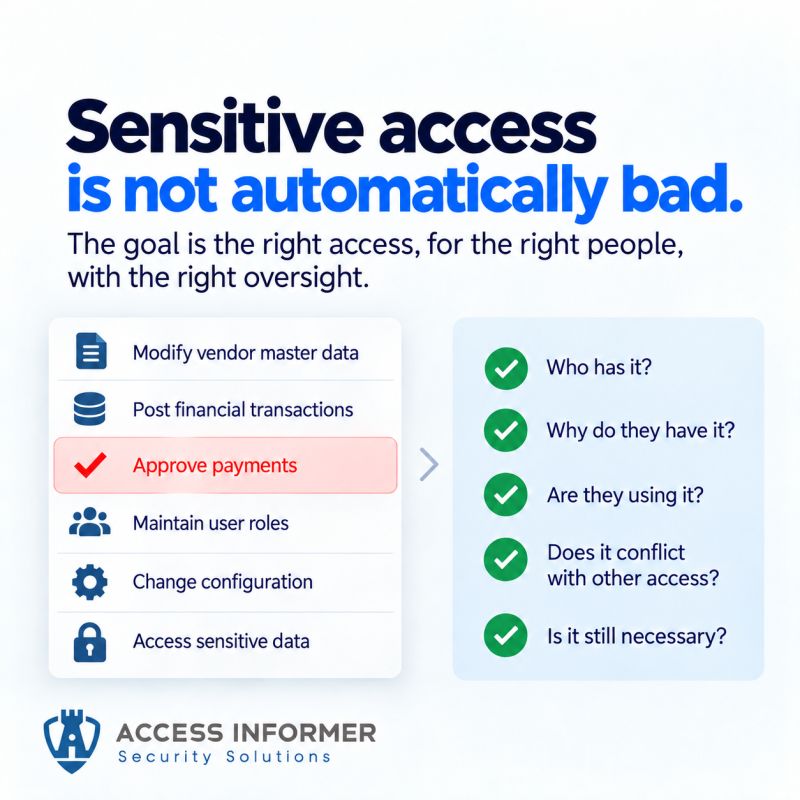
I don’t believe the goal of SAP security should be to eliminate sensitive access.
That wouldn’t be realistic.
People need to perform critical activities.
Someone has to:
• Create or change master data
• Approve transactions
• Administer roles
• Maintain configuration
• Access sensitive business information
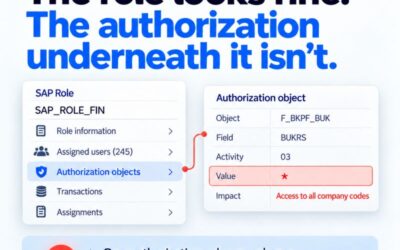
The real question is whether that access is 𝗮𝗽𝗽𝗿𝗼𝗽𝗿𝗶𝗮𝘁𝗲, 𝘂𝗻𝗱𝗲𝗿𝘀𝘁𝗼𝗼𝗱, 𝗮𝗻𝗱 𝗰𝗼𝗻𝘁𝗿𝗼𝗹𝗹𝗲𝗱.
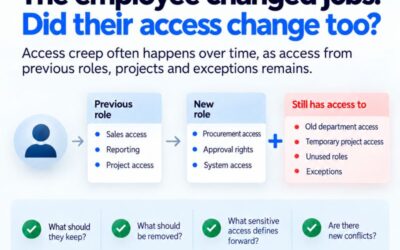
When I look at sensitive access, I want to know:
✅ Who has it?
✅ Why do they have it?
✅ Which role provides it?
✅ Are they actually using it?
✅ Does it conflict with other access?
✅ Is there still a valid business reason?
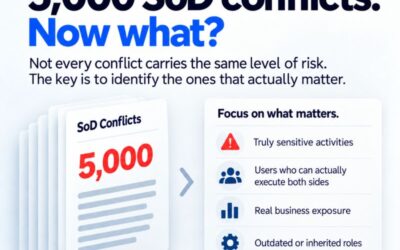
That is very different from simply generating a report of everyone who can perform a sensitive activity.
A long list is not necessarily a useful control.
Context matters.
The objective isn’t to remove every powerful permission.
The objective is to make sure powerful permissions exist 𝗳𝗼𝗿 𝘁𝗵𝗲 𝗿𝗶𝗴𝗵𝘁 𝗽𝗲𝗼𝗽𝗹𝗲, 𝗳𝗼𝗿 𝘁𝗵𝗲 𝗿𝗶𝗴𝗵𝘁 𝗿𝗲𝗮𝘀𝗼𝗻𝘀, 𝘄𝗶𝘁𝗵 𝘁𝗵𝗲 𝗿𝗶𝗴𝗵𝘁 𝗹𝗲𝘃𝗲𝗹 𝗼𝗳 𝗼𝘃𝗲𝗿𝘀𝗶𝗴𝗵𝘁.
That is where sensitive-access reviews become useful instead of just administrative.