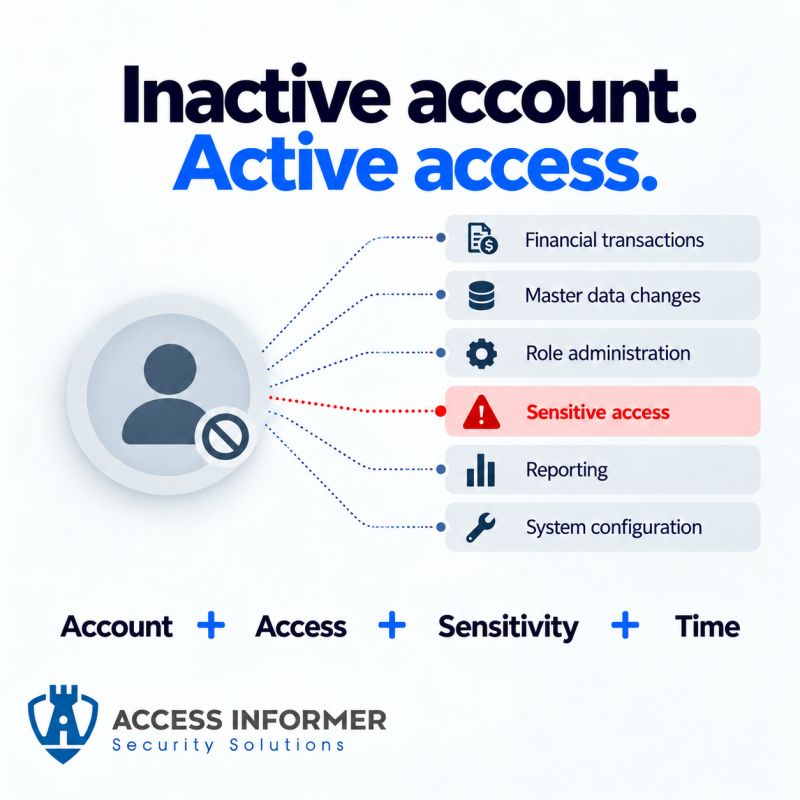
Dormant accounts are easy to categorize as a cleanup problem.
An account hasn’t been used.
Someone should probably remove it.
Put it on the backlog.
Move on.
But I think that misses the bigger question:
𝗪𝗵𝗮𝘁 𝗮𝗰𝗰𝗲𝘀𝘀 𝗱𝗼𝗲𝘀 𝘁𝗵𝗲 𝗮𝗰𝗰𝗼𝘂𝗻𝘁 𝘀𝘁𝗶𝗹𝗹 𝗵𝗮𝘃𝗲?
An unused account with very limited access is one thing.
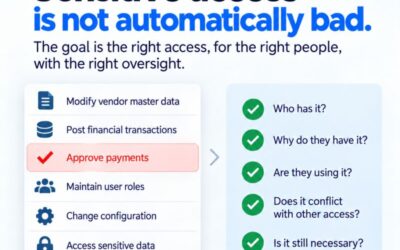
An unused account that can perform sensitive activities is something completely different.
The same applies to orphaned accounts.
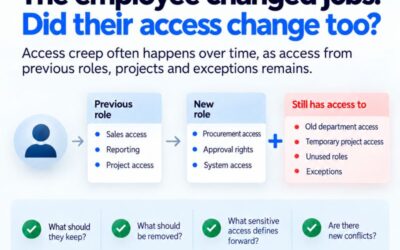
Someone leaves the organization.
Someone changes roles.
An external consultant finishes a project.
An account remains.
The account itself isn’t necessarily the critical finding.
It’s the combination of:
• Account
• Access
• Sensitivity
• Time
That’s what matters.
And that is why simply producing a list of inactive users isn’t enough.
You need to understand:
✅ What those accounts can actually do
✅ How long they’ve been inactive
✅ Which roles are still assigned
✅ Whether the access is sensitive
✅ Whether it conflicts with other access
✅ Whether there is any legitimate reason for it to remain
This is one of the areas we look at when assessing an SAP environment.
Not because every dormant account represents a major risk.
But because occasionally, one does.
And those are the ones worth finding.