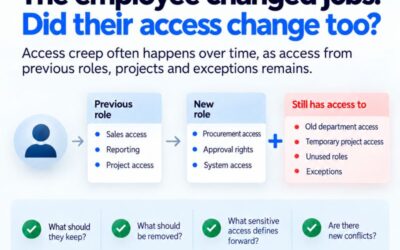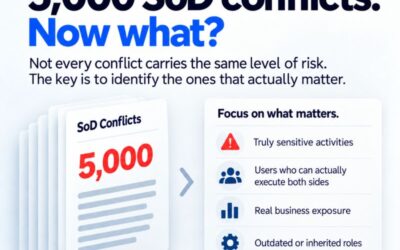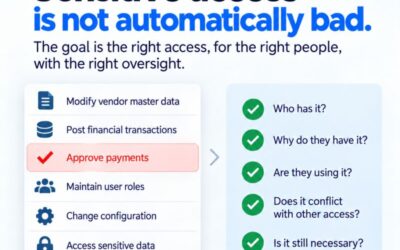
A role change can look harmless.
A new transaction.
A new authorization object.
A new assignment.
A small adjustment to support a project.
Then it goes live.
And suddenly:
❌ Sensitive access appears
❌ New SoD conflicts are introduced
❌ More users are affected than expected
❌ A temporary project fix becomes permanent
At that point, you’re no longer evaluating risk.
You’re cleaning it up.
That is why one of the most valuable questions in SAP security is:
“𝗪𝗵𝗮𝘁 𝘄𝗶𝗹𝗹 𝘁𝗵𝗶𝘀 𝗰𝗵𝗮𝗻𝗴𝗲 𝗱𝗼 𝗯𝗲𝗳𝗼𝗿𝗲 𝘄𝗲 𝗺𝗮𝗸𝗲 𝗶𝘁?”
Before transporting a role change, you should be able to understand:
✅ Which users will be affected
✅ Which sensitive activities will become available
✅ Which SoD conflicts will appear
✅ Whether existing controls will be weakened
✅ Whether the change creates downstream licensing or compliance impact
This doesn’t eliminate change.
It makes change safer.
The goal isn’t to slow projects down.
It’s to stop avoidable access problems from becoming production problems.